OU Delegation Permissions Reports
5 ReportsAbout OU Delegation Permissions Reports
OU Delegation Permissions Reports audit the security permissions assigned to Organizational Unit objects in Active Directory. Review who has been delegated administrative control over OUs, including the ability to manage users, groups, computers, and other objects within each OU.
Review all OU permissions
Inherited vs explicit rights
Find over-privileged access
Example: OU Delegation Permissions Reports in AD Reports
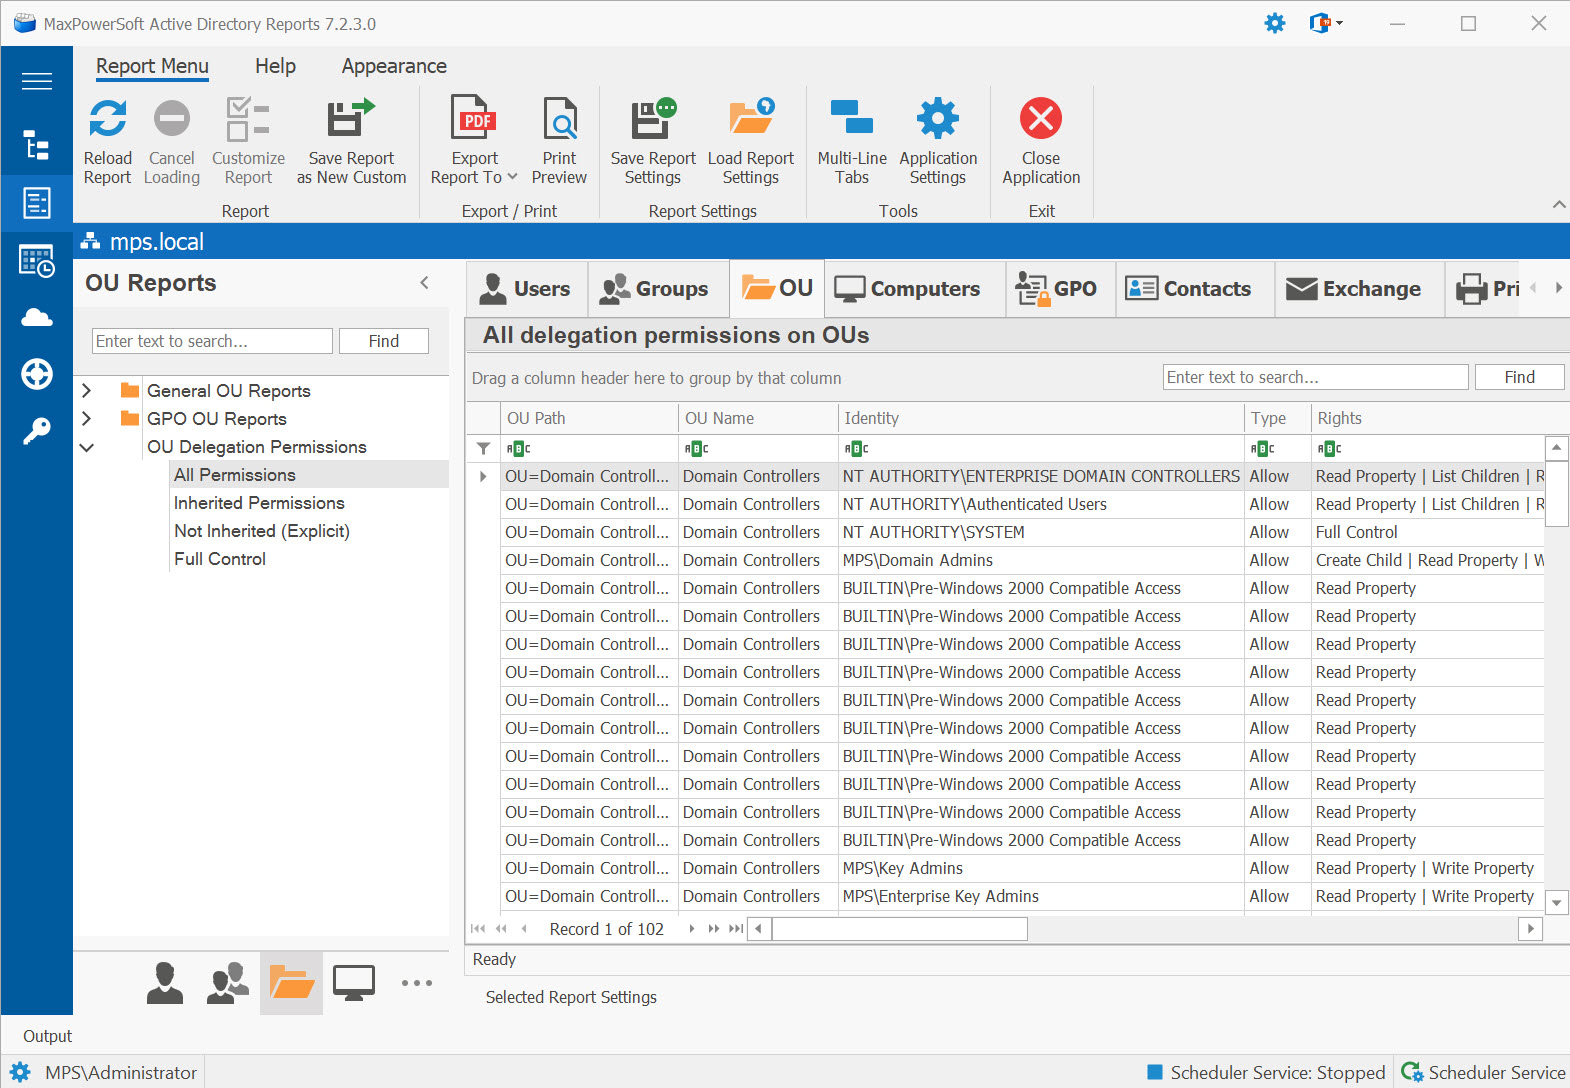
Available Reports
All Permissions
All delegation permissions on OUs. Provides a complete list of every permission entry on Organizational Unit objects, combining inherited and explicitly set permissions.
Use Cases
- Full OU permission audit baseline
- SOX / compliance access reviews
- Privilege review before AD restructuring
- Identify non-standard delegations
Key Information
- OU Distinguished Name
- Trustee (account or group)
- Permission type (read/write/full)
- Inheritance flag and object class scope
Inherited Permissions
Inherited delegation permissions on OUs. Shows permissions that flow down from parent containers via the AD inheritance model.
Use Cases
- Understand permission flow from parent OUs or domain root
- Verify expected inheritance hasn't been broken
- Establish permission baseline for new OU structures
Key Information
- Source container (origin of the inherited permission)
- Trustee account or group
- Permission type
- Propagation scope
Not Inherited (Explicit)
Explicitly set delegation permissions on OUs. These permissions were manually configured directly on OU objects, representing intentional administrative delegation decisions.
Use Cases
- Detect custom delegations granted without documentation
- Identify OUs with non-standard access models
- Change tracking for compliance audits
Key Information
- Trustee account or group
- Explicit permission type
- Object class restriction (user/computer/all)
- OU Distinguished Name
Full Control
Full Control delegation permissions on OUs. Identifies all accounts that have complete administrative control over OU objects and all child objects within them.
Use Cases
- Identify accounts with unrestricted control over an OU's objects
- Priority review for least-privilege enforcement
- Detect privilege escalation risks
- Tier 0 administrator access validation
Key Information
- Trustee account name and type (user/group)
- OU Distinguished Name
- Applied-to scope (this object / all descendant objects)
- Inheritance flag
Who can change New in 7.6.1
Every account that can change an OU you choose, or the objects in it — Full Control, writing properties, creating or deleting objects, resetting passwords, reading LAPS passwords, changing permissions — with the group it holds the right through. Members of delegated groups are listed one by one.
Use Cases
- Answer “who can change this OU?” for an audit
- Find accounts that can reset passwords or read LAPS passwords
- Review delegation before handing an OU to a team
- Detect privilege escalation paths through delegated groups
Key Information
- One row per account and permission entry: access, rights and what they apply to
- Granted To, how the account gets the right and the path through groups
- Domain New in 7.6.3 — tells apart accounts of the same name in two domains of the forest
- Whether the entry is inherited; Deny entries are listed
- Read-only rights are left out; a delegated group with no members shows as “(no members)”
- Groups from other domains of the forest are expanded too
See These Reports in Action
Try AD Reports free for 14 days — run any of these reports on your own Active Directory.
Download Free Trial View All Features